Zealience logo
prEN 40000-1-2 · prEN 40000-1-3 · prEN 40000-1-4 · EN IEC 62443-4-1

Cyber Resilience Act Compliance,
Automated.

Z-CMS automates your Cyber Resilience Act compliance — risk assessment, gap analysis, vulnerability handling policies, threat modelling and much more, based on official draft standards prEN 40000 and EN IEC 62443 series.

Understanding the regulation

What is the Cyber Resilience Act?

The Cyber Resilience Act (CRA) is the EU's cybersecurity regulation for all products with digital elements. It requires manufacturers to build in security by design, assess risks, handle vulnerabilities throughout the product lifecycle and maintain technical documentation.

  • Hardware
  • Software
  • Connected devices

The CRA timeline

  1. 10 Dec 2024

    Entry into force (applies)

  2. 11 Jun 2026

    Notified body rules (applies)

  3. 11 Sep 2026

    Reporting obligations (applies)

  4. Today
  5. 11 Dec 2027

    Full application

From 11 Dec 2027

Full application

442 days to go

Risk Assessment

Identify risks related to assets in your product

  • EN 40000-1-2
  • EN IEC 62443-4-1

Vulnerability Handling

Handle vulnerabilities across the product lifecycle

  • EN 40000-1-3

Product Requirements

Build in the required security controls

  • EN 40000-1-4
  • EN IEC 62443-4-2
  • Vertical: EN 304 xxx, EN 50xxx

User Documentation

Give users the information set out in Annex II

  • CRA Annex II

Reporting obligations have applied since 11 September 2026. Notifications go directly to ENISA's Single Reporting Platform, as the CRA requires. Read our reporting guide

Sound familiar?

Why CRA compliance is hard

Knowing the requirements is one thing. Turning them into evidence for every product is where most teams get stuck.

A tangle of CRA standards with a question mark at its centreprEN 40000-1-2EN IEC 62443-4-1CRA Annex IprEN 40000-1-4Article 13prEN 40000-1-3?

“We don’t know where to even start.”

prEN 40000-1-2, 1-3, 1-4, EN IEC 62443-4-1, the CRA annexes… The standards are dense, still in draft, and nobody tells you how they fit together or which parts apply to your product.

With Z-CMS: A guided Q&A built on the standards tells you what applies and what to do next.
A towering pile of documents next to a spinning clock

“Technical documentation takes forever.”

Risk assessments, gap analyses, vulnerability handling policies, technical files. Writing them from a blank page can take hundreds of hours of your experts’ time.

With Z-CMS: Reports and policies are generated from your answers, not written from scratch.

Six different products, each with its own fan of compliance documents, some with errors!!

“We have too many products to do this by hand.”

Every product in your portfolio that falls under the CRA is its own compliance project. Doing them one by one by hand doesn’t scale, and every team ends up with a different result.

With Z-CMS: One repeatable process for every product in your portfolio, with consistent, reproducible output.

Z-CMS turns all three into one guided, repeatable workflow.

See how it works

How Z-CMS solves it

How Z-CMS Automates CRA Compliance

Three features, each built on the official draft standards and guided step by step. More features are coming.

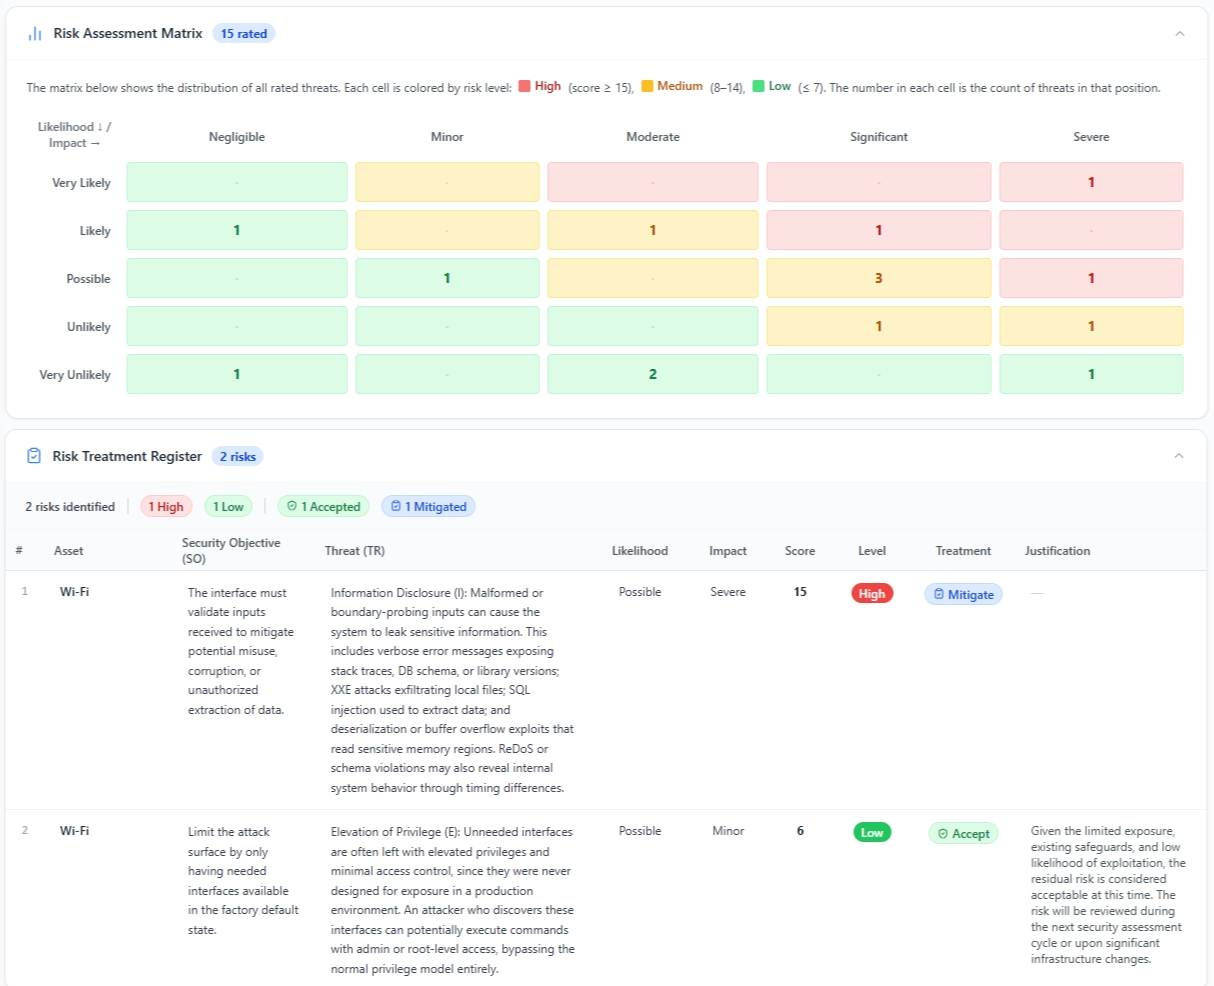
Risk Assessment & Threat Modelling

A guided Q&A that takes you through the full CRA risk assessment, from your product’s assets to the requirements that apply.

  • Identify the assets in your product that need protecting
  • Model threats and define security objectives in the same workflow
  • Pinpoint the CRA essential requirements that apply to your product
Based on prEN 40000-1-2EN IEC 62443-4-1
Learn more about risk assessment
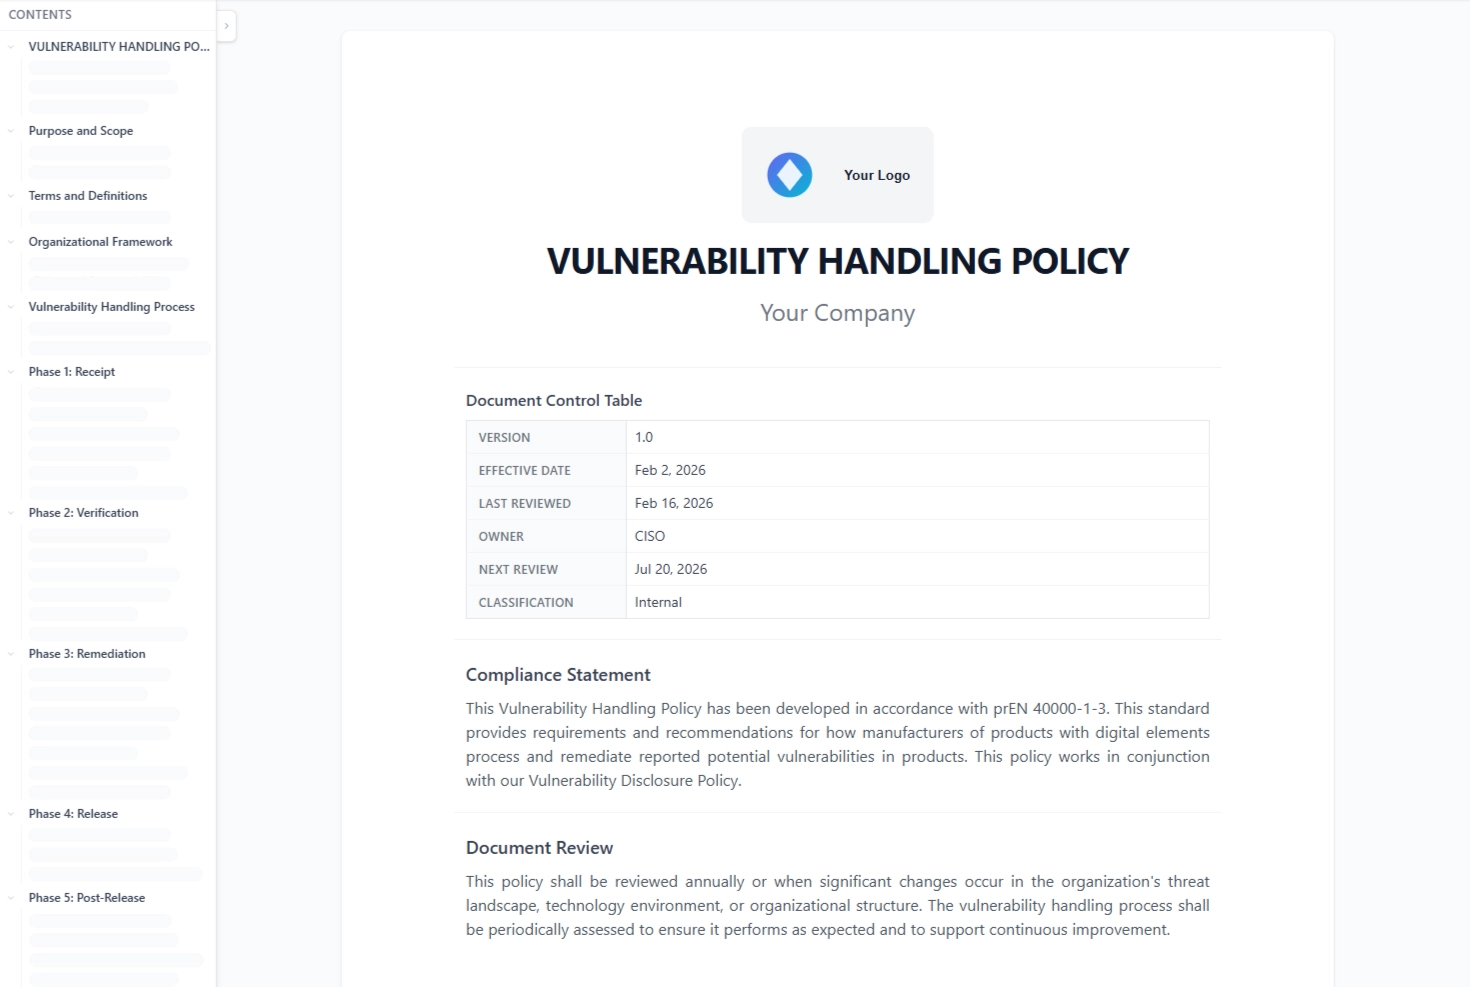
Z-CMS CRA risk assessment and threat modelling

Vulnerability Handling Policy Generator

Generate a complete vulnerability handling policy in minutes instead of writing it from scratch.

  • Built from expert-written templates
  • Fully customisable to your organisation
  • Saves hundreds of hours of drafting
Based on prEN 40000-1-3
Learn more about vulnerability handling
Z-CMS CRA vulnerability handling policy generator

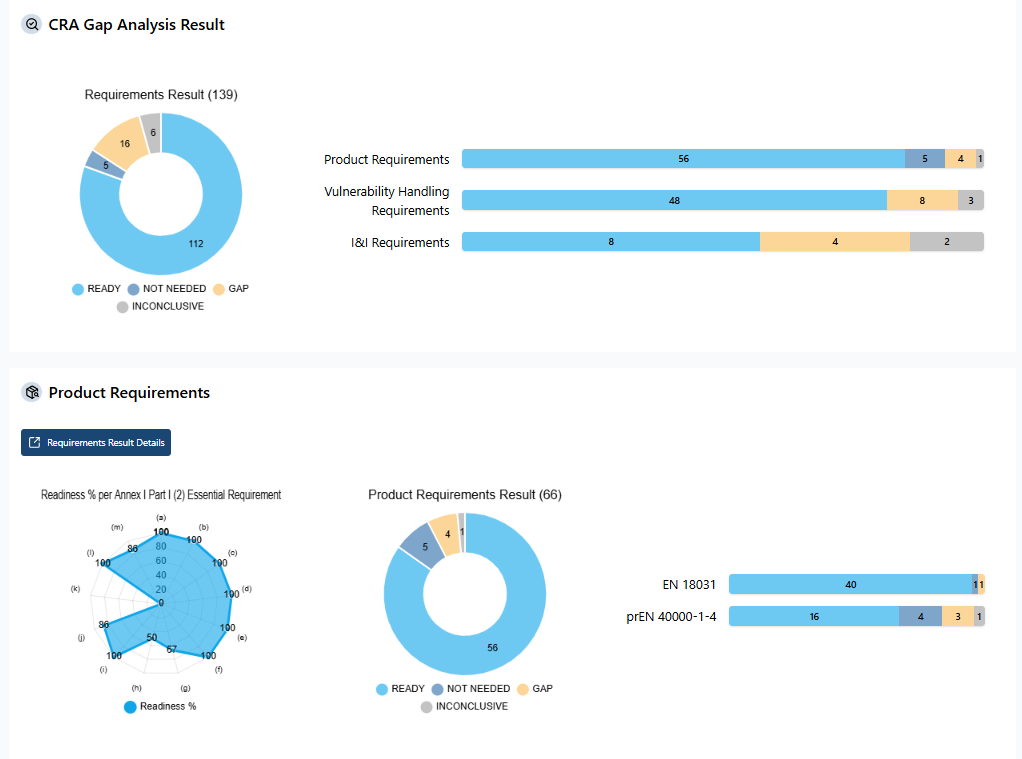
CRA Gap Analysis

A quick intelligent Q&A that measures your product’s readiness against the standards and the CRA text, and shows exactly where the gaps are.

  • Covers product requirements, vulnerability handling and user documentation
  • Real-time dashboard with exportable PDF reports
  • Built on EN 18031, so your RED DA work carries straight over
Based on EN 18031prEN 40000-1-4prEN 40000-1-3CRA Annex II
Learn more about CRA gap analysis
Z-CMS CRA gap analysis dashboard

Coming soon: as the standards mature, we're implementing full support for product requirements (prEN 40000-1-4, EN IEC 62443-4-2) and user documentation (CRA Annex II) in Z-CMS.

Why Z-CMS

Why choose Z-CMS for CRA compliance?

Built by IoT cybersecurity compliance experts, trusted by manufacturers worldwide for EN 18031 and now Cyber Resilience Act compliance.

Proven track record

100+

manufacturers brought to EN 18031 compliance

  • Self-assessed
  • Certified by Notified Bodies

“Z-CMS has been a great resource for developing real cybersecurity expertise.”

Ela Innovation
Dr. Guillaume Dupont

Expert leadership

Dr. Guillaume Dupont

Leads R&D, former tester at a global testing lab

In a field where interpretation errors lead to costly non-compliance, expert guidance is critical. Z-CMS is built on over a decade of IoT cybersecurity and compliance experience.

On-premises & flexible deployment

Your data never leaves your environment. Z-CMS runs entirely on infrastructure you control, on-premises or in your own private cloud, and needs no internet connectivity to operate. Zealience has no access: no SaaS analytics, no AI training, no external processing.

Our secure deployment
Z-CMS and your data inside infrastructure you control, on-premises or in your own private cloud. No data is sent out to the internet, and Zealience has no access.Your infrastructureZ-CMSYour dataDeploy asOn-premisesorPrivate cloudInternetNo data sent outNo accessZealience

Industry network

Zealience connects you to trusted consultants, legal experts and Notified Bodies, for end-to-end Cyber Resilience Act compliance support in a field where expertise is scarce.

View services
Zealience connects your team to consultants, legal experts and Notified BodiesYour teamConsultantsLegal expertsNotified BodiesZealience

FAQ

Questions about CRA compliance

Can't find what you're looking for? Our team is happy to walk you through your specific products and obligations.

Ask us directly
Does the Cyber Resilience Act apply to my product?

The CRA applies to products with digital elements placed on the EU market: hardware and software that connect, directly or indirectly, to a device or network. Products already covered by certain sector-specific EU rules, such as medical devices, motor vehicles and civil aviation, are excluded. Once a product is in scope, the Z-CMS risk assessment determines which essential requirements apply to it.

When do the CRA obligations apply?

Reporting obligations for actively exploited vulnerabilities and severe incidents apply since 11 September 2026. Most other obligations, including the risk assessment, vulnerability handling, product requirements and user documentation, apply from 11 December 2027.

Is Z-CMS based on final standards?

The harmonised standards for the CRA are still being finalised. Z-CMS is built on the official drafts prEN 40000-1-2, prEN 40000-1-3 and prEN 40000-1-4, as well as EN IEC 62443-4-1, and we update it as the standards are finalised.

What does Z-CMS cover for the CRA today?

Risk assessment with built-in threat modelling (prEN 40000-1-2, EN IEC 62443-4-1), a vulnerability handling policy generator (prEN 40000-1-3), and a gap analysis that checks your product’s readiness against EN 18031, prEN 40000-1-4, prEN 40000-1-3 and CRA Annex II. Full support for product requirements and user documentation is coming as the standards mature.

Can I report vulnerabilities and incidents through Z-CMS?

No, and that is deliberate. The CRA requires manufacturers to notify actively exploited vulnerabilities and severe incidents through ENISA’s Single Reporting Platform (SRP). We recommend reporting there directly rather than through any third-party software.

Read our reporting guide
Can I reuse my RED DA / EN 18031 work?

Yes. About two-thirds of EN 18031 is expected to be reused in prEN 40000-1-4, and Z-CMS covers both RED DA and the CRA, so the work you have already done gives you a head start. You can reuse information you have declared for EN 18031 for the CRA compliance.

Where is my data stored?

In your own environment. Z-CMS runs fully within your infrastructure, either on-prem or in your own cloud. Zealience has no access to your data: no SaaS analytics, no AI training and no external processing.

Our secure deployment
Can you help with conformity assessment and Notified Bodies?

Zealience connects you to trusted consultants, legal experts and Notified Bodies, for end-to-end support beyond the software.

View services

CRA full application in 442 days

Ready to start your
Cyber Resilience Act compliance journey?

See Z-CMS in a live demo with our founders, tailored to your products and your questions.

  1. 1

    Send a demo request

    One click opens an email to our team.

  2. 2

    Pick a time

    We reply with a booking link so you can choose a slot.

  3. 3

    Get a tailored live demo

    1 to 1.5 hours with our founders, built around your products and your questions.

  • 100+ manufacturers brought to EN 18031 compliance
  • Many customers certified by Notified Bodies
  • Your data stays in your environment