Zealience logo
Cyber Resilience Act compliance
Z-CMS Feature

CRA Risk Assessment, Automated.
Every Asset, Threat and Treatment Covered.

Risk assessment required by 11 December 2027

The risk assessment is the first step of Cyber Resilience Act compliance — it decides which essential requirements apply to your product. Z-CMS walks you through it with a guided Q&A: declare your assets, get the relevant threats, score them against your own criteria and record your treatments, in line with prEN 40000-1-2 and EN IEC 62443-4-1. Z-CMS then generates the technical documentation for you: an Excel risk assessment workbook and data flow diagrams of your product.

prEN 40000-1-2 EN IEC 62443-4-1 MITRE EMB3D
Watch the workflow

Where CRA compliance starts

What a CRA risk assessment has to cover

The Cyber Resilience Act is risk-based: how far the essential requirements in Annex I apply to your product depends on what your risk assessment says. EN 40000-1-2, the horizontal standard currently published as the draft prEN 40000-1-2, sets out the framework: what a risk assessment must cover. EN IEC 62443-4-1 follows the same framework, with slightly different terminology. Neither tells you step by step how to carry it out — that part is left to you. Here is what both ask for.

Product context

Describe the product, its intended use, its operating environment and its interfaces — the scope everything else is assessed against.

Risk acceptance criteria

Define how you rate risk and where your acceptance threshold sits, before you start scoring anything.

Asset and threat identification

Identify everything in the product worth protecting, then the threats that apply to each asset. Threats are identified per asset, so an incomplete asset list means an incomplete assessment.

Risk scoring and treatment

Rate each threat on likelihood and impact and compare it against your threshold. Every risk above it needs a treatment and a justification; accepted risks need a justification too.

Applicable requirements

Based on the risks you identified, determine which CRA essential requirements — and which requirements of standards such as prEN 40000-1-4 — you need to implement to address them.

Technical documentation

Two documents prove the assessment was done: one recording the risk assessment results with the product's architecture and design, and a graphical representation of that architecture to support threat modelling.

Z-CMS covers all six.

Its methodology is tailored to prEN 40000-1-2 and EN IEC 62443-4-1, and it guides you through every requirement to collect the information the standard asks for — mostly through intelligent Q&A, so you answer questions about your product instead of filling in templates. From your answers, it then generates both technical documents for you: an Excel workbook and data flow diagrams.

The workflow

From assets to treated risks

Seven steps, in the order the standards ask for them. The guided Q&A does the heavy lifting on the two steps manufacturers find hardest: working out what the assets are, and working out which threats apply to each one. The last step, the documentation, is generated for you.

  1. Start from the configurable 5×5 matrix and calibrate the ratings to your product. This is the step EN 40000-1-2 and EN IEC 62443-4-1 require before any risk is scored.

Threat modelling, built in

Threat modelling, without the whiteboard

Threat modelling means working out what an attacker could target, how, and which threats matter most — before anyone exploits them. It is usually treated as a specialist exercise. In Z-CMS it is part of the risk assessment: your engineers answer questions about the product they built, and Z-CMS does the modelling.

The traditional way

Workshops and whiteboards

  • A security specialist, in-house or external, has to lead the exercise
  • Architecture, attack paths and threats are drawn by hand
  • Coverage depends on who happens to be in the room
  • Hard to repeat for every product and every release

Built into Z-CMS

Just fill in questionnaires

  • Your engineers do it — nobody knows the product better
  • They fill in questionnaires: no diagrams, no security background needed
  • Every asset is checked against 120+ built-in threats
  • Threats land straight in the risk register, ready to rate

Comprehensive, repeatable, reproducible

Comprehensive

Every asset and every threat is properly documented, and each asset is checked against the full catalogue of 120+ threats — nothing depends on what someone happens to remember.

Repeatable

The same guided process for every product and every release, so the next assessment is as thorough as the first.

Reproducible

Same answers, same threats — whoever runs the assessment. Results you can explain to an auditor.

Every threat modelling activity, done systematically

  1. 1

    Identify what to protect

    Assets picked from the same curated list, every time

  2. 2

    Identify threats

    Every asset checked systematically against 120+ threats

  3. 3

    Analyse

    Likelihood and impact rated against your defined criteria

  4. 4

    Prioritise

    Your threshold decides what needs treatment — consistently

120+

built-in threats checked against every asset

EMB3D

MITRE EMB3D plus proprietary Zealience threats

0

architecture diagrams to draw

Risk assessment has traditionally been work for cybersecurity experts. That doesn't scale under the CRA, where every product with digital elements needs one, kept up to date for its whole support period. That's why we built Z-CMS: to equip the engineers who build your products to carry out the risk assessment themselves.

Proof of conformance

The documents that prove compliance, generated for you

EN 40000-1-2 and EN IEC 62443-4-1 don't just ask you to carry out a risk assessment — they ask you to document it. Without these documents at hand, you cannot claim compliance. Z-CMS generates both of them automatically from the answers you have already given.

Excel workbook

Risk assessment and architecture

Everything an auditor needs to follow your assessment, in one structured workbook.

  • Risk assessment results: assets, threats, ratings, treatments and justifications
  • Your product's architecture and design
  • Laid out for prEN 40000-1-2 and EN IEC 62443-4-1
Compliant with prEN 40000-1-2EN IEC 62443-4-1

Data flow diagrams

Your architecture, drawn for you

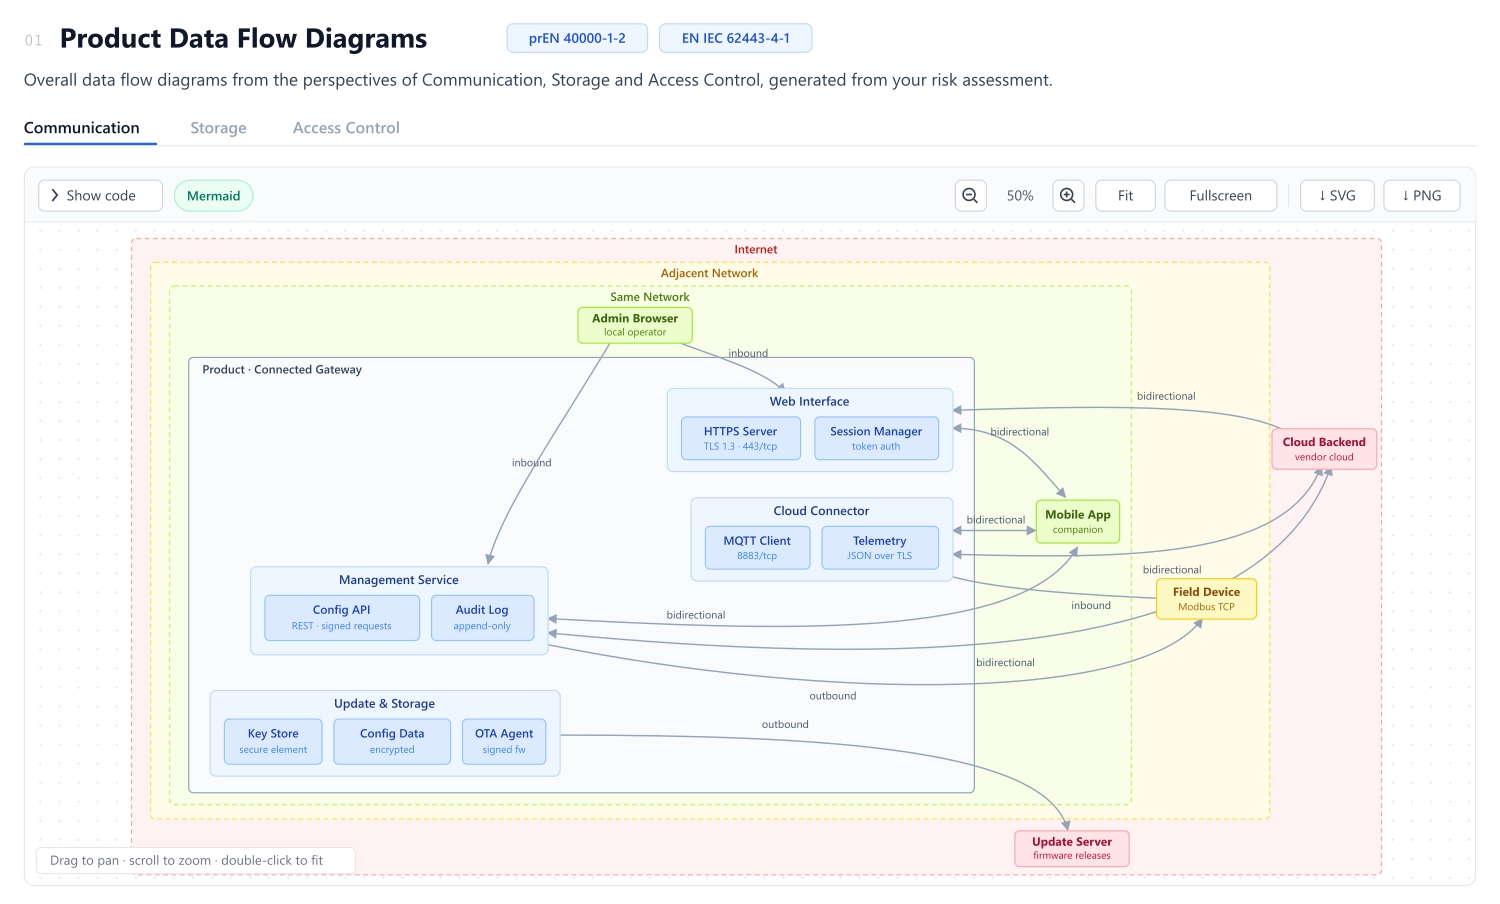
Diagrams of your product’s assets, their relationships and how they are used, to support threat modelling.

  • Communication, storage and access control views, plus how every asset relates to the others
  • Review them in Z-CMS before you export
  • Export as SVG, PNG, or the complete Mermaid code in a .md file — portable to any docs tool
Compliant with prEN 40000-1-2EN IEC 62443-4-1

No spreadsheet to build. No diagrams to draw.

All you need to do is answer the questionnaires in Z-CMS, from top to bottom. Z-CMS takes it from there.

  1. You answer the questionnaires in Z-CMS, top to bottom

  2. Z-CMS builds the Excel workbook and the data flow diagrams

  3. You download your proof of conformance, ready to file

Common questions

CRA risk assessment FAQ

Ready to start your
CRA risk assessment?

See the full workflow on your own product — acceptance criteria, asset Q&A, threat identification from MITRE EMB3D, risk register and treatments — in a personalised demo. Or explore our pricing.

View Pricing

Trusted by manufacturers worldwide

prEN 40000-1-2 & EN IEC 62443-4-1
Free Customer Support
On-Premises Security